Content governance
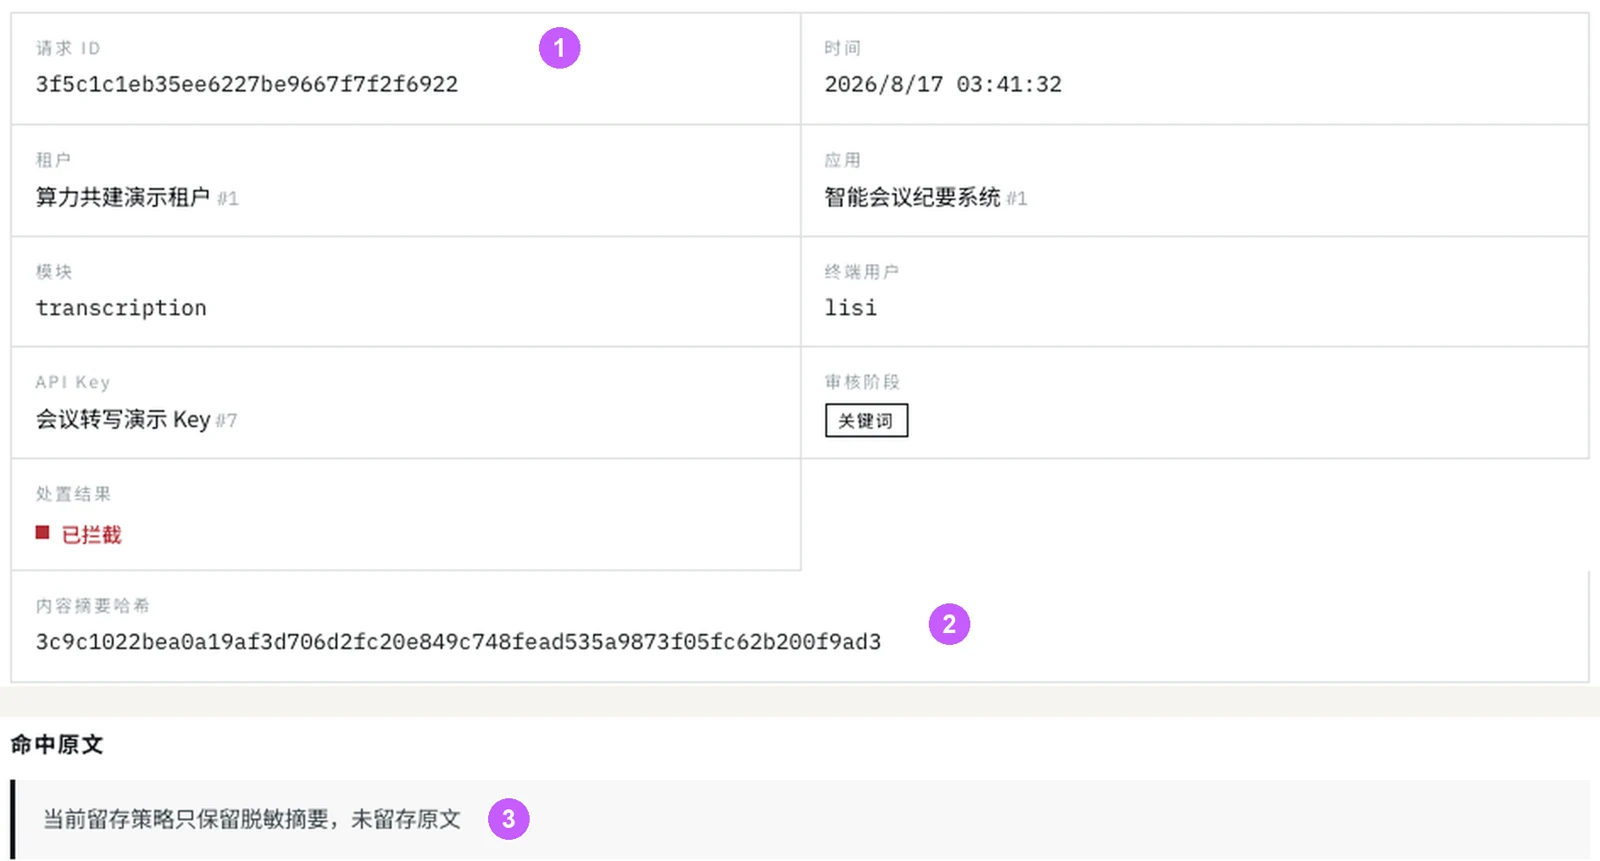
Apply observation or blocking modes, moderation policies and word lists; link findings to call attribution.
AIGW sits between business applications and model or HTTP services, governing AI and general API calls with shared identity, policies and auditing, plus content moderation, usage attribution and upstream routing.
Content reviewed · v2.0.00
01 / Capabilities
Enterprise and public-sector AI teams, platform operators, shared-compute partners and organizations opening APIs to internal or external consumers.
Apply observation or blocking modes, moderation policies and word lists; link findings to call attribution.
Distinguish caller-supplied labels from signed identities. Map verified identities to employees, departments and applications.
Inspect usage dimensions, organizational snapshots and locked periods. Keep AI Token accounts separate from API byte and latency records.
Manage model aliases, upstream pools and forwarding using capacity, health and routing policies.
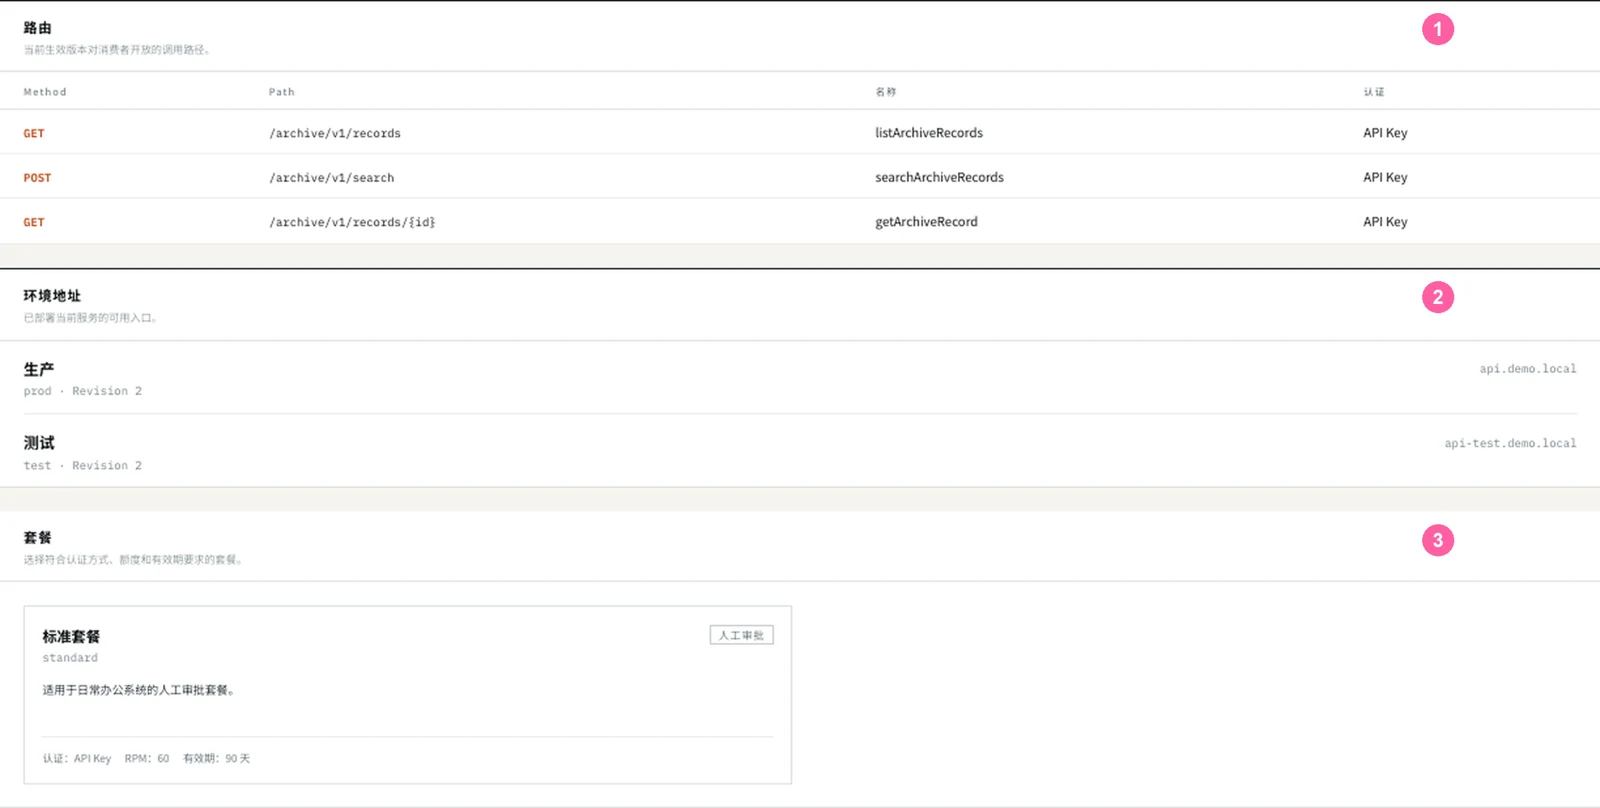
Govern HTTP access with published catalogs, subscriptions and policies, retaining access records and explanations.
Manage both data planes through one control plane with common identity, API keys, permissions and auditing.
02 / Workflow
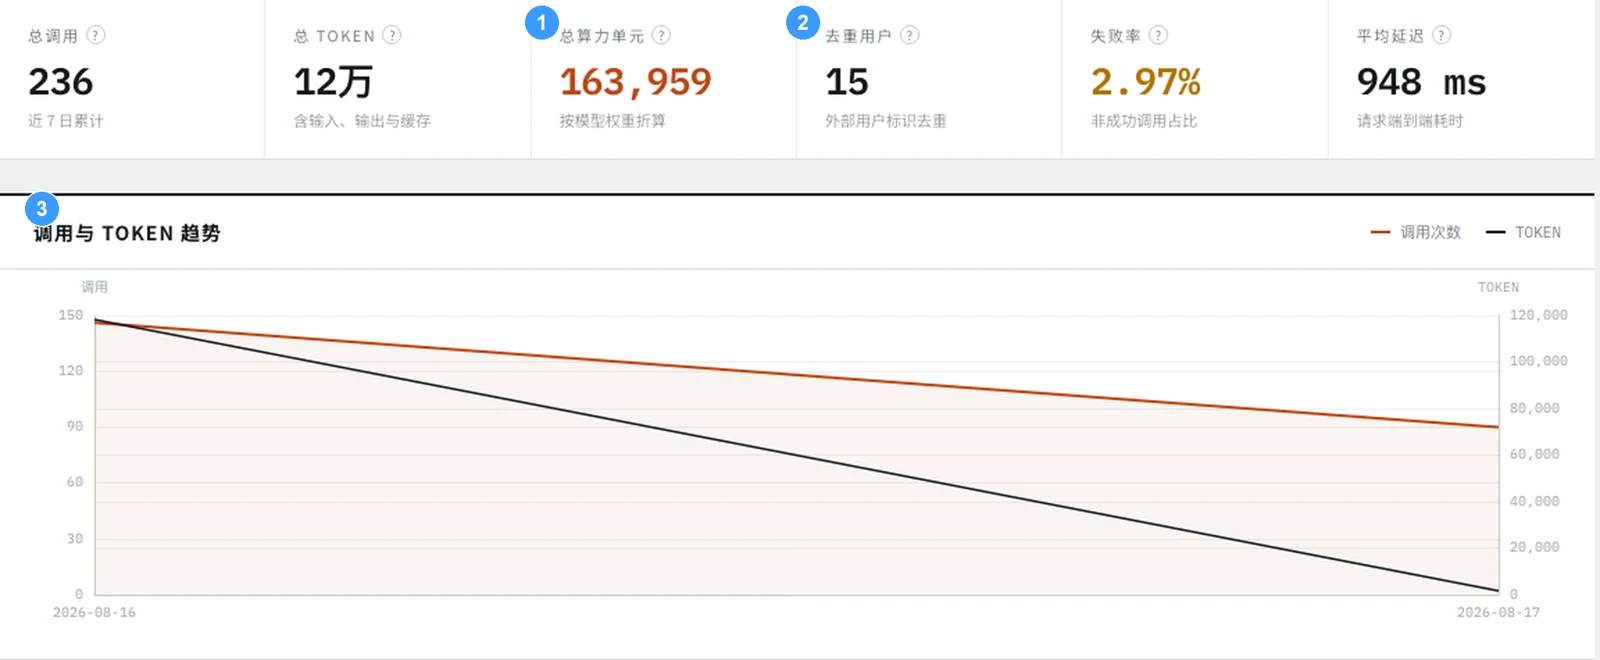
When departments share an AI application, the upstream service often sees only one application key. AIGW brings identity and organization into the request governance flow and reports usage by user, department and application. Trusted attribution requires the signed identity contract. Caller-supplied user labels alone support statistical attribution, not verified identity.
03 / Product screenshot
04 / Deployment & scope
Private delivery is supported. AI and general API data planes share a control plane; general API features are off by default and enabled when needed. Agree on identity sources, upstreams, policies, metering and cluster needs.
Moderation depends on configured policies and services and cannot guarantee detection of every risk. General API governance does not replace every role of an existing gateway. Laboratory benchmarks do not establish customer production performance.
05 / FAQ
AIGW
No. v2.0.00 supports AI and general HTTP API governance. The general API data plane is disabled by default and enabled as needed.
No. Unsigned body fields and headers are caller assertions. Trusted attribution requires a verifiable signed identity and correct organizational mappings.
No. AI calls record Token usage; general APIs record bytes, latency and other access metrics. Allocation or monetary billing follows tenant configuration and delivery scope.
06 / Resources
PDFs are in Chinese. Document versions may differ from web content; check the date and version.
HONGCHUANGDA TECHNOLOGY
Three independent products, deployable separately. Cross-product integration is scoped per project.